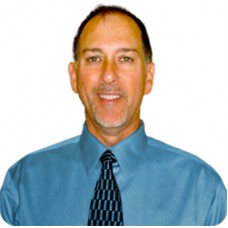
- Speaker : David Nettleton
- Session Code : DNNOV1026
- Date : 10th November 2026
- Time : 1:00 PM Eastern Time / 10:00 AM Pacific Time
- Duration : 75 Mins
The 6 Most Common FDA Software Validation Failures and How to Prevent Them
Overview:
One
of the most concerning findings during an FDA inspection is discovering that an
electronic record can be modified without a reliable history of what changed,
who made the change, or why. In a March 2026 Warning Letter, FDA identified
electronic batch-record modifications made through a software vendor without
corresponding audit trail entries. Another Warning Letter issued in May
highlighted unvalidated laboratory software, missing audit trail controls, and
inadequate protection of electronic test data. These findings illustrate how
weaknesses in computerized system controls can compromise data integrity,
undermine confidence in validation practices, and expose manufacturers to
significant regulatory consequences.
The
regulatory environment has also evolved. In February 2026, FDA issued revised
final guidance on Computer Software Assurance for medical device production and
quality management system software, reinforcing a risk-based approach to
establishing confidence in computerized systems. The implementation of the
Quality Management System Regulation (QMSR) introduced a revised inspection
framework for medical device manufacturers, while pharmaceutical companies
continue to face scrutiny over computerized system controls, electronic
records, and data integrity. These developments bring renewed attention to the
decisions organizations make when validating software and maintaining evidence
of compliance.
For
validation professionals, the challenges often begin with determining what
needs to be validated and how much testing is appropriate. Organizations must
establish which systems and electronic records fall within the scope of 21 CFR
Part 11 or EU Annex 11, verify security controls, audit trails, and electronic
signatures, and evaluate the responsibilities associated with locally
installed, SaaS, and cloud-hosted applications. Unclear requirements,
inadequate project staffing, poorly defined vendor responsibilities, and
inconsistent testing practices can result in unnecessary documentation,
implementation delays, and compliance gaps that remain undiscovered until an
audit or inspection.
This
webinar will examine the six most common problems encountered in FDA software
validation and verification and explain practical strategies for avoiding them.
David Nettleton will address critical considerations for regulated software
systems, including electronic record requirements, security and audit trail
functionality, different software hosting environments, and effective
validation project staffing. The discussion will also explore why sound
validation practices make business sense by reducing avoidable project costs,
rework, and the need for corrective action.
For
professionals responsible for validating, implementing, maintaining, or
overseeing computerized systems, understanding these recurring problems can
help improve project planning, strengthen validation documentation, and support
more consistent compliance decisions. The session will provide practical
guidance for identifying weaknesses before they become costly findings,
maintaining defensible validation evidence, and reducing exposure to FDA Form
483 observations and Warning Letters.
Areas
covered in the session:
- Which
data and systems are subject to 21 CFR Part 11 and Annex 11
- Why
compliance makes good business sense.
- Details
of FDA regulations/system features as applied to software: security, audit
trails, electronic signatures.
- Requirements
for local, SaaS, and cloud hosting
- The 6
Most Common Problems in FDA Software Validation & Verification.
- Strategies
on how to avoid the most common problems.
- Advice
on successful validation project staffing.
- Avoid
483 and Warning Letters.
Why
Should You Attend?
Software
validation problems can remain hidden for months or even years, only to surface
during an FDA inspection, system upgrade, or investigation involving electronic
records. By that point, correcting the deficiencies may require extensive
remediation, additional testing, revised documentation, and significant
resources. Understanding where validation projects commonly fail can help
organizations identify weaknesses earlier, make better decisions about system
controls, and maintain reliable evidence of compliance.
This
webinar will help attendees evaluate their existing validation practices and
recognize gaps involving 21 CFR Part 11, EU Annex 11, security controls, audit
trails, electronic signatures, and software hosting arrangements. Participants
will gain a clearer understanding of how to approach validation planning,
determine appropriate project resources, avoid unnecessary testing and
documentation burdens, and address recurring problems that can undermine
inspection readiness. These considerations are particularly valuable for
organizations implementing new systems, transitioning to SaaS or cloud-based
applications, or maintaining established computerized systems.
Drawing
on his extensive experience in FDA-regulated computerized systems, David
Nettleton will examine six recurring validation and verification problems and
share practical strategies for preventing them. Attendees will leave with a
better understanding of where to focus their validation efforts, how to
strengthen the reliability of their supporting documentation, and what steps
can help reduce the likelihood of FDA Form 483 observations, Warning Letters,
and costly corrective actions.
Who
Will Benefit?
This
webinar is intended for professionals responsible for software validation,
computerized system compliance, data integrity, and the implementation and
maintenance of FDA-regulated systems. It is particularly relevant to
individuals working in pharmaceutical, biotechnology, medical device, and other
FDA-regulated organizations. Those include:
- Computer
System Validation (CSV) Managers
- Computer
System Validation (CSV) Specialists
- Computer
Software Assurance (CSA) Professionals
- Software
Validation Engineers
- Software
Verification and Validation (V&V) Engineers
- Validation
Managers
- Validation
Engineers
- Quality
Assurance (QA) Managers
- Quality
Assurance (QA) Specialists
- Quality
Systems Managers
- Quality
Compliance Managers
- Regulatory
Compliance Managers
- Data
Integrity Managers and Specialists
- 21
CFR Part 11 Compliance Specialists
- GxP
Compliance Managers and Specialists
- IT
Quality Assurance Managers
- IT
Compliance Managers
- GxP
IT Managers
- Computerized
Systems Managers
- Laboratory
Information Management System (LIMS) Administrators
- Manufacturing
Execution System (MES) Managers
- Electronic
Quality Management System (eQMS) Administrators
- Laboratory
and Manufacturing Systems Validation Specialists
- Software
Implementation and Validation Project Managers
- Quality
and Regulatory Auditors
Computer System Validation’s principal, David Nettleton is an industry leader, author, and teacher for 21 CFR Part 11, Annex 11, HIPAA, EU General Data Protection Regulation (GDPR), software validation, and computer system validation. He is involved with the development, purchase, installation, operation and maintenance of computerized systems used in FDA compliant applications. He has completed more than 300 mission critical laboratory, clinical, and manufacturing software implementation projects. His most recent book is Software as a Service (SaaS) Risk-Based Validation With Time-Saving Templates, which provides fill-in-the-blank templates for completing a COTS software validation project.
Enrollment Options
Tags: FDA Software Validation, Software Verification, Computer System Validation, CSV, Computer Software Assurance, CSA, 21 CFR Part 11, EU Annex 11, GxP Compliance, Software Validation Problems, Data Integrity, Audit Trails, Electronic Signatures, SaaS Validation, Cloud Validation, FDA 483, FDA Inspection Readiness, Validation Best Practices, FDA Compliance 2026, David, Nettleton, November 2026